Do Solo Businesses Need a Cybersecurity Plan? NIST Just Published One
Published 4 November 2026
Who is responsible for cybersecurity at a business with no IT department and no employees besides the owner?
The National Institute of Standards and Technology (NIST) answered that question on November 2, 2026, with a new publication called "Small Business Cybersecurity: Non-Employer Firms" (NIST Cybersecurity White Paper 50). It is written for freelancers, sole proprietors and independent contractors, a group NIST says makes up more than 28 million businesses in the United States. According to Help Net Security's coverage of the release, non-employer firms account for about 82% of the 34.8 million small businesses nationwide.
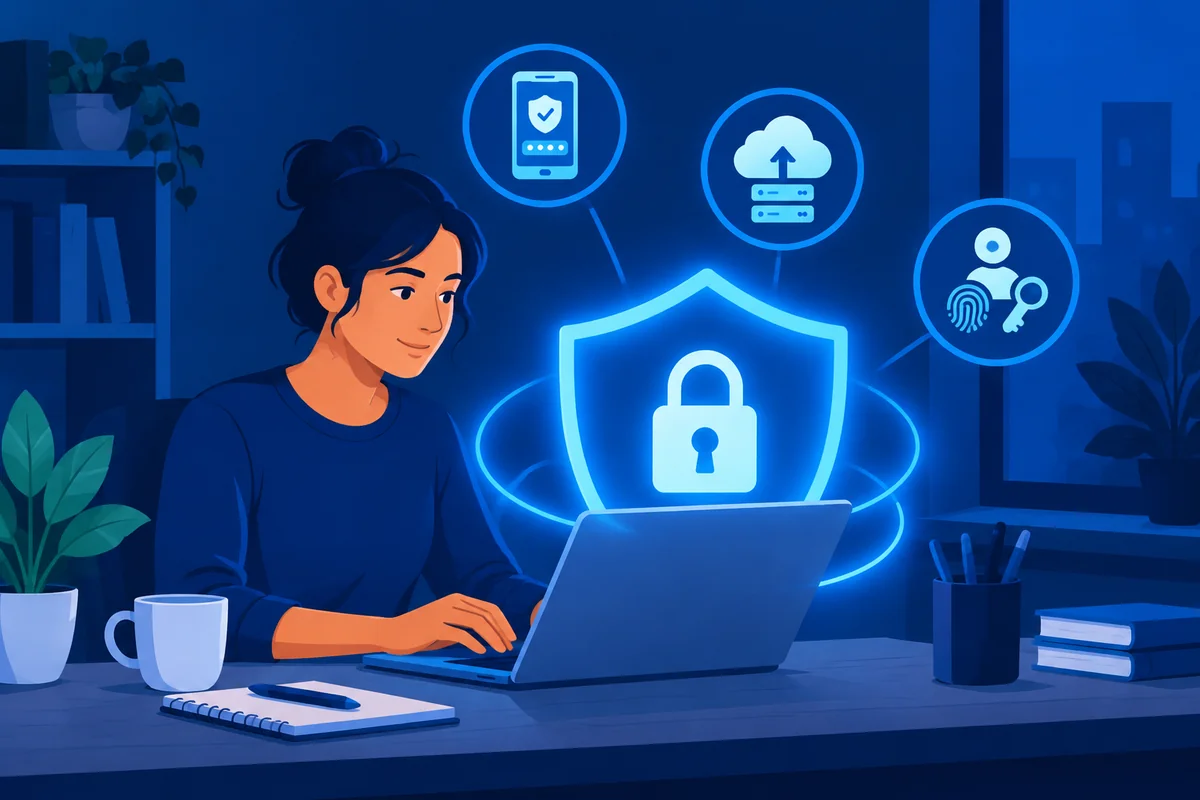
The guide maps its advice to the NIST Cybersecurity Framework 2.0 but drops the jargon. It recommends enabling multi-factor authentication on every account that offers it, using phishing-resistant MFA for email, banking and cloud storage, and turning on passkeys where available. For accounts that still rely on passwords, it recommends unique passphrases of at least 15 characters. It also tells owners to back up data regularly and actually test the backups, keep software updated, and learn to recognize phishing and ransomware attempts.
The guide also addresses a newer risk: using AI tools in day-to-day work. It recommends reviewing how an AI provider stores or shares data before entering anything sensitive, and checking AI-generated content before sharing it or acting on it. NIST's Daniel Eliot said the goal was advice owners "can implement... on their own with limited technical knowledge or with minimal financial investment."
This matters because a huge share of U.S. businesses look exactly like this: one person, a laptop, a handful of cloud accounts and no security team. A single compromised email account or an unbacked-up laptop can stop the business cold, and most of the fixes NIST describes cost nothing but time.
What you can do this week
- Turn on multi-factor authentication for your email, banking and cloud storage accounts, and switch to passkeys where they're offered.
- Set up or test a backup of your business files, and confirm you could actually restore from it.
- Write down which AI tools you use and what customer or business data you've entered into them, then check each provider's data policy.
If your business relies on a customer portal, booking system or other custom software, security works best when it is built in from the start rather than bolted on later. That is one of the things we focus on at Zamorins when we build custom software for clients, alongside the basic habits in NIST's guide.
Takeaway: You do not need a security budget to follow most of NIST's new guidance, just an hour this week to turn on MFA, check your backups and review where your data is going.
Sources
- Self-Employed? Solopreneur? NIST Has a Cybersecurity Guide Just for You, NIST (November 2, 2026)
- NIST publishes cybersecurity guide for businesses too small to have IT staff, Help Net Security (November 4, 2026)